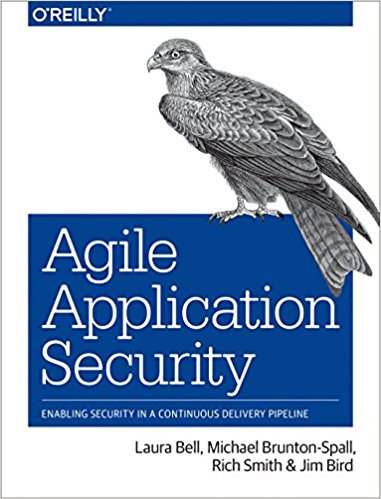
Agile Application Security
Enabling Security in a Continuous Delivery Pipeline
About the book
Agile development and traditional security management have rarely fitted together, so security experts and agile veterans Laura Bell, Michael Brunton-Spall, Rich Smith and Jim Bird set out to bridge the two. The guide begins by teaching each side the other's principles. It shows how to build security practices into every stage of an existing development lifecycle, from planning, requirements and design down to the code, and how to make security testing part of delivering working software in every release. Other topics are regulatory compliance in agile or DevOps settings and a security program built on empathy, openness, transparency and collaboration. The authors also describe problems from their own agile security work and how they tried to solve them.
In an interview, PentesterLab founder Louis Nyffenegger listed it among the books on his bedside table.
We hope you love the books people recommend! Just so you know, The CEO Library may collect a share of sales or other compensation from the links on this page.
This book has 1 recommendation
Recommended by Louis Nyffenegger (Founder/PentesterLab)
Source: Interview with Louis Nyffenegger
Get this book on Amazon | Barnes & Noble | Apple Books
See more books recommended by
See more books written by
Laura Bell, Michael Brunton-Spall, Rich Smith, Jim Bird